#php

382 posts · Last used 12h

📣 PHP security releases are scheduled for Thursday, 19 November 2026, 14:00–14:30 UTC, as part of our regular four-week release cycle. All supported PHP versions are affected. Highest severity: CRITICAL. Issues at this severity require non-default configuration or uncommon setups. Please prepare to upgrade promptly once the releases are available. 🔗 https://www.php.net/archive/2026.php#2026-11-18-1 #PHP #Release #Security

23
0
80
0
Hello, fediverse 👋 This account posts every PHP, Composer and WordPress vulnerability that gets added to CISA's Known Exploited Vulnerabilities list: what's affected, the fixed version, and a link to the advisory. It's the short list that matters: today 36 of about 19,500 PHP vulnerabilities are known to be exploited. Posts are automatic. I'm Oroma, I build phpwarden (an open-source PHP vulnerability scanner) and I read the replies. #PHP #WordPress #infosec #introduction
1
0
2
0
🆕 blog! “Blunt Banhammer Blocks Basic Bots Ballistically” I cut bot traffic to my site by over 80% with a simple trap. Last month, my hobby website OpenBenches.org transferred more than 2.5TB of data to visitors. As much as I'd like to think the site is enormously popular, it looks like it is just AI bots endlessly crawling the data and… 👀 Read more: https://shkspr.mobi/blog/2026/11/blunt-banhammer-blocks-basic-bots-ballistically/ ⸻ #AI #bot #CyberSecurity #NaBloPoMo #PHP #WebDev
6
0
3
0
Even schaamteloos eigen werk promoten (voel je vooral niet verplicht te klikken). Ik heb na de #PHP-ellende van vorige week voor @NRC@nrc.social een verhaal gemaakt over #OpenSource en de financiering daarvan. Drie keer raden waar het lukte om contact te leggen met de hoofdpersoon @edorian@phpc.social. Dank ook aan @ronnylam@mastodon.social en @Brenno@mastodon.social https://www.nrc.nl/nieuws/2026/10/29/opeens-moest-de-slecht-gefinancieerde-stichting-achter-programmeertaal-php-keihard-aan-de-bak-a4939870 @wlaatje@social.edu.nl
73
0
57
0
Steal my #Bitcoin There is a bitcoin key hidden on this server worth about $2,014. It is accessible to the PHP user account through the print-flag binary. This #PHP version was selected from before the #PHP2SHELL CVEs were released. https://stealmybitcoin.com/ EDIT: Just wanted to clarify that this is not my initiative and I’m not affiliated with it. Sorry if my original post suggested otherwise, it was a quick copy/paste from the website (which seems to be down since several hours, by the way). I simply saw the link and I liked the idea.
82
0
68
1
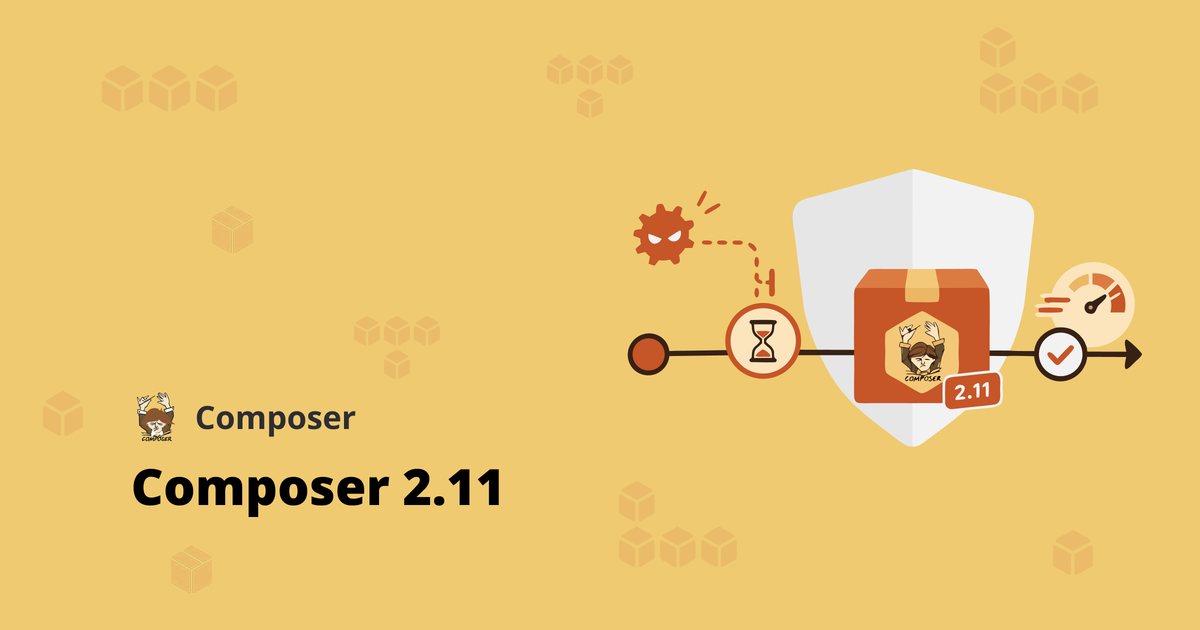
Composer 2.11 is out 🚀 cooldown dependency policies hold back freshly published package versions for an hour or a day, so compromised releases can be flagged before they reach your composer update. Composer 2.11 includes several security fixes, block-scope support for custom dependency policies, OSC 7501 terminal progress reporting and faster and more memory efficient dependency resolution. Full blog post: https://blog.packagist.com/composer-2-11-release/ #php #phpc #composerphp #supplychainsecurity
24
1
23
0
There isn't an easy exploit for this PHP vulnerability I came across the link via https://mastodon.social/@CuratedHackerNews/117481600704689796 Last time I touched php it was ~20 years ago and maybe for a month. Could someone with actual php understanding weigh in? Somehow, somewhere between the lines, my understanding was that there have been observances of the vuln being used in the wild before the 14 UTC. And that wasn’t from reading news sites
0
5
0
0
Replying to
None of my posts on Bluesky ever get shared much. If you’re there, I’d appreciate a boost, please. 🙏 https://bsky.app/profile/ramsey.dev/post/3myx25vdrsrq2 #PHP
0
0
1
0
Hi Fediverse 👋 I'm Kevin, a PHP/Symfony developer and team lead from Germany. Lately one question keeps me busy: how do you let AI coding agents write PHP without lowering the bar? My answer so far: quality gates first. PHPStan at max, Rector, ECS, tests, architecture rules, Infection. I write about it at https://blog.tony-stark.xyz and share my templates on GitHub. Happy to swap notes! #introduction #PHP #Symfony #PHPStan
0
0
1
0

Set session.upload_progress.enabled=0 until the next PHP release to block an unlikely RCE vector (CVE-2026-115560).

We already recommended this for CVE-2026-109619 from Wednesday: keep it disabled.

Only applications with non-default serialize_handler switching it to php at runtime can be affected.

There is more information in the advisory on the PHP website by the PHP security team: https://www.php.net/archive/2026.php#2026-10-23-1

#php

92
7
161
7
(1/5) Some thoughts on yesterday's #PHP #vulnerability 🔒 Normally, vulnerabilities are patched before we hear about them, with key distributors notified in advance to reduce risk. This time, a security researcher accidentally published details early, and a for-profit PHP distributor broke embargo and leaked the fix. The vulnerability was exploited in the wild within the hour, making everything worse.
20
17
15
0